
 Worksheets
C7 - Quiz
Total questions: 21
Worksheet time: 21mins
Which protocol creates a virtual point-to-point connection to tunnel unencrypted traffic between Cisco routers from a variety of protocols?
OSPF
IPsec
IKE
GRE
Which is a requirement of a site-to-site VPN?
It requires a client/server architecture.
It requires the placement of a VPN server at the edge of the company network.
It requires hosts to use VPN client software to encapsulate traffic.
It requires a VPN gateway at each end of the tunnel to encrypt and decrypt traffic.
Which two statements describe a remote access VPN? (Choose two.)
It connects entire networks to each other.
It requires hosts to send TCP/IP traffic through a VPN gateway.
It is used to connect individual hosts securely to a company network over the Internet.
It may require VPN client software on hosts.
It requires static configuration of the VPN tunnel.
Two corporations have just completed a merger. The network engineer has been asked to connect the two corporate networks without the expense of leased lines. Which solution would be the most cost effective method of providing a proper and secure connection between the two corporate networks?
Cisco AnyConnect Secure Mobility Client with SSL
Cisco Secure Mobility Clientless SSL VPN
Frame Relay
remote access VPN using IPsec
site-to-site VPN
Which two scenarios are examples of remote access VPNs? (Choose two.)
A toy manufacturer has a permanent VPN connection to one of its parts suppliers.
All users at a large branch office can access company resources through a single VPN connection.
A mobile sales agent is connecting to the company network via the Internet connection at a hotel.
A small branch office with three employees has a Cisco ASA that is used to create a VPN connection to the HQ.
An employee who is working from home uses VPN client software on a laptop in order to connect to the company network.
Which statement describes the effect of key length in deterring an attacker from hacking through an encryption key?
The length of a key will not vary between encryption algorithms.
The length of a key does not affect the degree of security.
The shorter the key, the harder it is to break.
The longer the key, the more key possibilities exist.
Which statement accurately describes a characteristic of IPsec?
IPsec works at the application layer and protects all application data.
IPsec works at the transport layer and protects data at the network layer.
IPsec is a framework of open standards that relies on existing algorithms.
IPsec is a framework of proprietary standards that depend on Cisco specific algorithms.
IPsec is a framework of standards developed by Cisco that relies on OSI algorithms.
How is "tunneling" accomplished in a VPN?
New headers from one or more VPN protocols encapsulate the original packets.
All packets between two hosts are assigned to a single physical medium to ensure that the packets are kept private.
Packets are disguised to look like other types of traffic so that they will be ignored by potential attackers.
A dedicated circuit is established between the source and destination devices for the duration of the connection.
Which two statements describe the IPsec protocol framework? (Choose two.)
AH uses IP protocol 51.
AH provides encryption and integrity.
AH provides integrity and authentication.
ESP uses UDP protocol 51.
AH provides both authentication and encryption.
What technology is used to negotiate security associations and calculate shared keys for an IPsec VPN tunnel?
3DES
IKE
PSK
SHA
What are the two modes used in IKE Phase 1? (Choose two.)
aggressive
main
passive
primary
secondary
What takes place during IKE Phase 2 when establishing an IPsec VPN?
IPsec security associations are exchanged.
Traffic is exchanged between IPsec peers.
ISAKMP security associations are exchanged.
Interesting traffic is identified.
What is a function of the GRE protocol?
to configure the set of encryption and hashing algorithms that will be used to transform the data sent through the IPsec tunnel
to encapsulate multiple OSI Layer 3 protocol packet types inside an IP tunnel
to configure the IPsec tunnel lifetime
to provide encryption through the IPsec tunnel
What type of traffic is supported by IPsec?
IPsec supports all traffic permitted through an ACL.
IPsec only supports unicast traffic.
IPsec supports all IPv4 traffic.
IPsec supports layer 2 multicast traffic.

Refer to the exhibit. What HMAC algorithm is being used to provide data integrity?
SHA
MD5
DH
AES
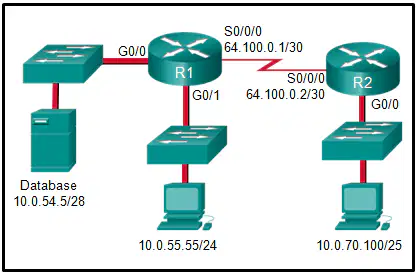
Refer to the exhibit. A VPN tunnel is configured on the WAN between R1 and R2. On which R1 interface(s) would a crypto map be applied in order to create a VPN between R1 and R2?
G0/0
G0/0 and G0/1
S0/0/0
all R1 interfaces
Router R1 has configured ISAKMP policies numbered 1, 5, 9, and 203. Router R2 only has default policies. How will R1 attempt to negotiate the IKE Phase 1 ISAKMP tunnel with R2?
R1 and R2 cannot match policies because the policy numbers are different.
R1 will attempt to match policy #1 with the most secure matching policy on R2.
R1 will begin to try to match policy #1 with policy #65514 on R2.
R1 will try to match policy #203 with the most secure default policy on R2.
Consider the following configuration on a Cisco ASA:
crypto ipsec transform-set ESP-DES-SHA esp-des esp-sha-hmac
What is the purpose of this command?
to define only the allowed encryption algorithms
to define the ISAKMP parameters that are used to establish the tunnel
to define what traffic is allowed through and protected by the tunnel
to define the encryption and integrity algorithms that are used to build the IPsec tunnel
What is needed to define interesting traffic in the creation of an IPsec tunnel?
access list
security associations
transform set
hashing algorithm
When the CLI is used to configure an ISR for a site-to-site VPN connection, what is the purpose of the crypto map command in interface configuration mode?
to bind the interface to the ISAKMP policy
to configure the transform set
to force IKE Phase 1 negotiations to begin
to negotiate the SA policy

Refer to the exhibit. What show command displays whether the securityk9 software is installed on the router and whether the EULA license has been activated?
show running-config
show version
show interfaces s0/0/0
show crypto isakmp policy 1

