
 Worksheets
IAS1-Assessment Test (BSIT3102)
Total questions: 20
Worksheet time: 10mins
The organization that Chris works for has disabled automatic updates. What is the most common reason for disabling automatic updates for organizational systems?
To avoid disruption of the work process for office workers
To prevent security breaches due to malicious patches and updates
To avoid issues with problematic patches and updates
All of the above
Which of the following is the least volatile according to the forensic order of volatility?
The system's routing table
Logs
Temp files
CPU registers
Ed wants to trick a user into connecting to his evil twin access point (AP). What type of attack should he conduct to increase his chances of the user connecting to it?
A disassociation attack
An application denial-of-service attack
A known plain-text attack
A network denial-of-service attack
What term is used to describe wireless site surveys that show the relative power of access points on a diagram of the building or facility?
Signal surveys
db maps
AP topologies
Heatmaps
What hardware device is used to create the hardware root of trust for modern desktops and laptops?
System memory
A HSM
The CPU
The TPM
Angela wants to prevent users in her organization from changing their passwords repeatedly after they have been changed so that they cannot reuse their current password. What two password security settings does she need to implement to make this occur?
Set a password history and a minimum password age.
Set a password history and a complexity setting.
Set a password minimum and maximum age.
Set password complexity and maximum age
Chris wants to establish a backup site that is fully ready to take over for full operations for his organization at any time. What type of site should he set up?
A cold site
A clone site
A hot site
A ready site
Which of the following is not a common constraint of embedded Technet24 and specialized systems?
Computational power
Overly complex firewall settings
Lack of network connectivity
Inability to patch
Gary is reviewing his system's SSH logs and sees logins for the user named “Gary” with passwords like password1, password2 … PassworD. What type of attack has Gary discovered?
A dictionary attack
A rainbow table attack
A pass-the-hash attack
A password spraying attack
Kathleen wants to set up a system that allows access into a high security zone from a low-security zone. What type of solution should she configure?
VDI
A container
A screened subnet
A jump server
Derek's organization is worried about a disgruntled employee publishing sensitive business information. What type of threat should Derek work to protect against?
Shoulder surfing
Social engineering
Insider threats
Phishing
Jeff is concerned about the effects that a ransomware attack might have on his organization and is designing a backup methodology that would allow the organization to quickly restore data after such an attack. What type of control is Jeff implementing?
Corrective
Preventive
Detective
Deterrent
Samantha is investigating a cybersecurity incident where an internal user used his computer to participate in a denial-of service attack against a third party. What type of policy was most likely violated?
BPA
SLA
AUP
MOU
Jean recently completed the user acceptance testing process and is getting her code ready to deploy. What environment should house her code before it is released for use?
Test
Production
Development
Staging
Rob has created a document that describes how staff in his organization can use organizationally owned devices, including if and when personal use is allowed. What type of policy has Rob created?
A change management policy
An acceptable use policy
An access control policy
A playbook
Oren obtained a certificate for his domain covering *.acmewidgets.net. Which one of the following domains would not be covered by this certificate?
Richard is sending a message to Grace and would like to apply a digital signature to the message before sending it. What key should he use to create the digital signature?
Richard's private key
Richard's public key
Grace's private key
Grace's public key
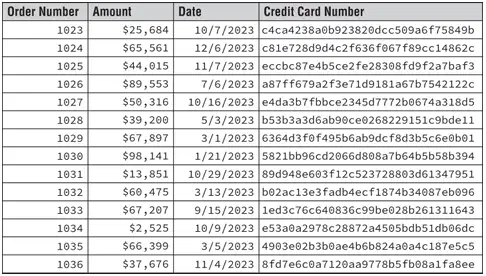
Stephanie is reviewing a customer transaction database and comes across the data table shown here. What data minimization technique has most likely been used to obscure the credit card information in this table?
Destruction
Masking
Hashing
Tokenization
Andrew is working with his financial team to purchase a cybersecurity insurance policy to cover the financial impact of a data breach. What type of risk management strategy is he using?
Risk avoidance
Risk transference
Risk acceptance
Risk mitigation
Shelly is writing a document that describes the steps that incident response teams will follow upon first notice of a potential incident. What type of document is she creating?
Guideline
Standard
Procedure
Policy

