
 Worksheets
MSSR-PRCT-SC+_A
Total questions: 108
Worksheet time: 57mins
Attacker obtains bank account number
and birth date by calling the victim
Vishing
Spoofing
On-path
DDoS
Hoax
Attacker modifies a legitimate DNS server to resolve
the IP address of a malicious site
Vishing
Spoofing
On-path
DDoS
Hoax
Attacker intercepts all communication between
a client and a web server
Vishing
Spoofing
On-path
DDoS
Hoax
Multiple attackers
overwhelm a web server
Vishing
Spoofing
On-path
DDoS
Hoax
A virus alert appears in your browser from Microsoft
with a phone number to call for support
Vishing
Spoofing
On-path
DDoS
Hoax
The security team at a local public library system is creating a set of
minimum security standards for the various computer systems.
Select the BEST security control for each available placeholder.
Location:
Library
Web Server and
Database Server
Description:
Computer Room
High security
Choose 3.
Locking Cabinets
Environmental Sensors
Video Surveillance
Full-Disk Encryption
Biometric Reader
The security team at a local public library system is creating a set of
minimum security standards for the various computer systems.
Select the BEST security control for each available placeholder.
Location:
Library
Employee
Laptops
Description:
Offsite use
Contains PII
Choose 2.
Locking Cabinets
Environmental Sensors
Video Surveillance
Full-Disk Encryption
Biometric Reader
The security team at a local public library system is creating a set of
minimum security standards for the various computer systems.
Select the BEST security control for each available placeholder.
Location:
Library
Lending
Systems
Description:
Manages the check-in
and check-out process
Choose 1.
Locking Cabinets
Smart Card
Video Surveillance
Full-Disk Encryption
Biometric Reader
The security team at a local public library system is creating a set of
minimum security standards for the various computer systems.
Select the BEST security control for each available placeholder.
Location:
Digital Newspaper
Reading Lab
Description:
Open Area
No supervision
Laptop computers
Choose 1.
Locking Cabinets
Smart Card
Video Surveillance
Full-Disk Encryption
Cable Lock
Choose the BEST secure network protocol
for the description:
Accept customer purchases from your primary website
HTTPS
NTPsec
SRTP
SNMPv3
SSH
Choose the BEST secure network protocol
for the description:
Synchronize the time across all of your devices
HTTPS
NTPsec
SRTP
SNMPv3
SSH
Choose the BEST secure network protocol
for the description:
Access your switch using a CLI terminal screen
HTTPS
NTPsec
SRTP
SNMPv3
SSH
Choose the BEST secure network protocol
for the description:
Talk with customers on scheduled conference calls
HTTPS
NTPsec
SRTP
SNMPv3
SSH
Choose the BEST secure network protocol
for the description:
Gather metrics from routers at remote sites
HTTPS
NTPsec
SRTP
SNMPv3
SSH
Match the appropriate authentication reference (Authentication Factor) to each description.
Each authentication factor or attribute will be used once.
Description:
During the login process, your phone receives a
text message with a one-time passcode
Something you can do
Somewhere you are
Something you have
Something you know
Something you are
Match the appropriate authentication reference (Authentication Factor) to each description.
Each authentication factor or attribute will be used once.
Description:
You enter your PIN to make
a deposit into an ATM
Something you can do
Somewhere you are
Something you have
Something you know
Something you are
Match the appropriate authentication reference (Authentication Factor) to each description.
Each authentication factor or attribute will be used once.
Description:
You must sign a check-in sheet
before entering a controlled area
Something you can do
Somewhere you are
Something you have
Something you know
Something you are
Match the appropriate authentication reference (Authentication Factor) to each description.
Each authentication factor or attribute will be used once.
Description:
You can use your ngerprint to unlock
the door to the data center
Something you can do
Somewhere you are
Something you have
Something you know
Something you are
Match the appropriate authentication reference (Authentication Factor) to each description.
Each authentication factor or attribute will be used once.
Description:
Your login will not work unless you are
connected to the VPN
Something you can do
Somewhere you are
Something you have
Something you know
Something you are
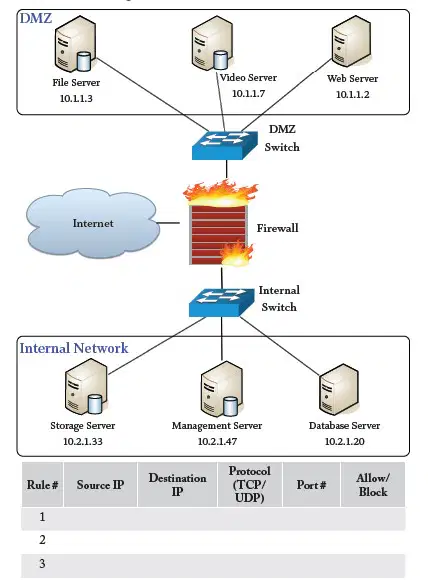
Configure the following stateful firewall rules:
• Allow the Web Server to access the Database Server using LDAP
Choose the correct answer (Source IP/Destination IP/Protocol[TCP/UDP]/Port #/Allow or Block)
Source: 10.1.1.2 / Destination: 10.2.1.20/ Protocol: TCP / Port 389 / Allow
Source: 10.2.1.33 / Destination: 10.1.1.7/ Protocol: TCP / Port 443 / Allow
Source: 10.2.1.47 / Destination: 10.1.1.3/ Protocol: TCP / Port 22 / Allow
Configure the following stateful firewall rules:
• Allow the Storage Server to transfer files to the Video Server
over HTTPS
Choose the correct answer (Source IP/Destination IP/Protocol[TCP/UDP]/Port #/Allow or Block)
Source: 10.1.1.2 / Destination: 10.2.1.20/ Protocol: TCP / Port 389 / Allow
Source: 10.2.1.33 / Destination: 10.1.1.7/ Protocol: TCP / Port 443 / Allow
Source: 10.2.1.47 / Destination: 10.1.1.3/ Protocol: TCP / Port 22 / Allow
Configure the following stateful firewall rules:
• Allow the Management Server to use a secure terminal on the
File Server
Choose the correct answer (Source IP/Destination IP/Protocol[TCP/UDP]/Port #/Allow or Block)
Source: 10.1.1.2 / Destination: 10.2.1.20/ Protocol: TCP / Port 389 / Allow
Source: 10.2.1.33 / Destination: 10.1.1.7/ Protocol: TCP / Port 443 / Allow
Source: 10.2.1.47 / Destination: 10.1.1.3/ Protocol: TCP / Port 22 / Allow
You’ve hired a third-party to gather information about your company’s
servers and data. The third-party will not have direct access to your
internal network but can gather information from any other source.
Which of the following would BEST describe this approach?
Backdoor testing
Passive footprinting
OS fingerprinting
Partially known environment
Which of these protocols use TLS to provide secure communication?
(Select TWO)
HTTPS
SSH
FTPS
SNMPv2
DNSSEC
Which of these threat actors would be MOST likely to attack systems for
direct financial gain?
Organized crime
Hacktivist
Nation state
Competitor
A security incident has occurred on a file server. Which of the following
data sources should be gathered to address file storage volatility?
(Select TWO)
Partition data
Kernel statistics
ROM data
Temporary file systems
Process table
An IPS at your company has found a sharp increase in traffic from
all-in-one printers. After researching, your security team has found a
vulnerability associated with these devices that allows the device to be
remotely controlled by a third-party. Which category would BEST
describe these devices?
IoT
RTOS
MFD
SoC
Which of the following standards provides information on privacy and
managing PII?
ISO 31000
ISO 27002
ISO 27701
ISO 27001
Elizabeth, a security administrator, is concerned about the potential for
data exfiltration using external storage drives. Which of the following
would be the BEST way to prevent this method of data exfiltration?
Create an operating system security policy to prevent
the use of removable media
Monitor removable media usage in host-based firewall logs
Only allow applications that do not use removable media
Define a removable media block rule in the UTM
A CISO (Chief Information Security Officer) would like to decrease
the response time when addressing security incidents. Unfortunately, the
company does not have the budget to hire additional security engineers.
Which of the following would assist the CISO with this requirement?
ISO 27701
PKI
IaaS
SOAR
An insurance company has created a set of policies to handle data
breaches. The security team has been given this set of requirements based
on these policies:
• Access records from all devices must be saved and archived
• Any data access outside of normal working hours
must be immediately reported
• Data access must only occur inside of the country
• Access logs and audit reports must be created from a single database
Which of the following should be implemented by the security team to
meet these requirements? (Select THREE)
Restrict login access by IP address and GPS location
Require government-issued identification
during the onboarding process
Add additional password complexity for accounts that access data
Consolidate all logs on a SIEM
Enable time-of-day restrictions on the authentication server
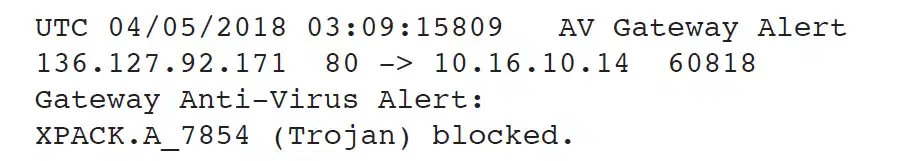
Rodney, a security engineer, is viewing this record from the firewall logs:
Which of the following can be observed from this log information?
The victim's IP address is 136.127.92.171
A download was blocked from a web server
A botnet DDoS attack was blocked
The Trojan was blocked, but the file was not
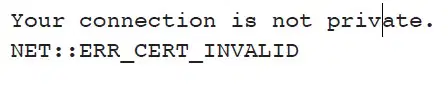
A user connects to a third-party website and receives this message:
Which of the following attacks would be the MOST likely reason
for this message?
Brute force
DoS
On-path
Disassociation
Which of the following would be the BEST way to provide a website
login using existing credentials from a third-party site?
Federation
802.1X
PEAP
EAP-FAST
A system administrator, Daniel, is working on a contract that will specify
a minimum required uptime for a set of Internet-facing firewalls. Daniel
needs to know how often the firewall hardware is expected to fail between
repairs. Which of the following would BEST describe this information?
MTBF
RTO
MTTR
MTTF
An attacker calls into a company’s help desk and pretends to be the
director of the company’s manufacturing department. The attacker
states that they have forgotten their password and they need to have the
password reset quickly for an important meeting. What kind of attack
would BEST describe this phone call?
Social engineering
Tailgating
Vishing
On-path
A security administrator has been using EAP-FAST wireless
authentication since the migration from WEP to WPA2. The company’s
network team now needs to support additional authentication protocols
inside of an encrypted tunnel. Which of the following would meet the
network team’s requirements?
EAP-TLS
PEAP
EAP-TTLS
EAP-MSCHAPv2
Which of the following would be commonly provided
by a CASB? (Select TWO)
List of all internal Windows devices that have not installed the
latest security patches
List of applications in use
Centralized log storage facility
List of network outages for the previous month
Verification of encrypted data transfers
The embedded OS in a company’s time clock appliance is configured to
reset the file system and reboot when a file system error occurs. On one
of the time clocks, this file system error occurs during the startup process
and causes the system to constantly reboot. Which of the following
BEST describes this issue?
DLL injection
Resource exhaustion
Race condition
Weak configuration
A recent audit has found that existing password policies do not include
any restrictions on password attempts, and users are not required to
periodically change their passwords. Which of the following would
correct these policy issues? (Select TWO)
Password complexity
Password expiration
Password history
Password lockout
Password recovery
What kind of security control is associated with a login banner?
Preventive
Deterrent
Corrective
Detective
Compensating
A security team has been provided with a non-credentialed vulnerability
scan report created by a third-party. Which of the following would they
expect to see on this report?
A summary of all files with invalid group assignments
A list of all unpatched operating system files
The version of web server software in use
A list of local user accounts
A business manager is documenting a set of steps for processing orders
if the primary Internet connection fails. Which of these would BEST
describe these steps?
Communication plan
Continuity of operations
Stakeholder management
Tabletop exercise
A security administrator is concerned about data exfiltration resulting
from the use of malicious phone charging stations. Which of the
following would be the BEST way to protect against this threat?
USB data blocker
Personal firewall
MFA
FDE
A company would like to protect the data stored on laptops used in
the field. Which of the following would be the BEST choice for this
requirement?
MAC
SED
CASB
SOAR
A file server has a full backup performed each Monday at 1 AM.
Incremental backups are performed at 1 AM on Tuesday, Wednesday,
Thursday, and Friday. The system administrator needs to perform a full
recovery of the file server on Thursday afternoon. How many backup sets
would be required to complete the recovery?
2
3
4
1
A company is creating a security policy that will protect all corporate
mobile devices:
• All mobile devices must be automatically locked after a predefined
time period.
• Some mobile devices will be used by the remote sales teams, so the
location of each device needs to be traceable.
• All of the user’s information should be completely separated from
company data.
Which of the following would be the BEST way to establish these
security policy rules?
Containerization
Biometrics
COPE
VDI
MDM
A security engineer runs a monthly vulnerability scan. The scan doesn’t
list any vulnerabilities for Windows servers, but a significant vulnerability
was announced last week and none of the servers are patched yet. Which
of the following best describes this result?
Exploit
Credentialed
Zero-day attack
False negative
A security administrator is adding additional authentication controls to
the existing infrastructure. Which of the following should be added by
the security administrator? (Select TWO)
TOTP
Least privilege
Role-based awareness training
Separation of duties
Smart Card
A network administrator would like each user to authenticate with
their personal username and password when connecting to the
company's wireless network. Which of the following should the network
administrator configure on the wireless access points?
WPA2-PSK
802.1X
WPS
WPA2-AES
A security administrator needs to identify all references to a Javascript
file in the HTML of a web page. Which of the following tools should be
used to view the source of the web page and search through the file for a
specific filename? (Select TWO)
tail
openssl
scanless
grep
curl
A user has assigned individual rights and permissions to a file on their
network drive. The user adds three additional individuals to have readonly
access to the file. Which of the following would describe this access
control model?
DAC
MAC
ABAC
RBAC
A remote user has received a text message requesting login details to the
corporate VPN server. Which of the following would BEST describe this
message?
Brute force
Prepending
Typosquatting
Smishing
A department store policy requires that a floor manager approves each
transaction when a gift certificate is used for payment. The security team
has found that some of these transactions have been processed without
the approval of a manager. Which of the following would provide a
separation of duties to enforce this store policy?
Use a WAF to monitor all gift certificate transactions
Disable all gift certificate transactions for cashiers
Implement a discretionary access control policy
Require an approval PIN for the cashier and a separate
approval PIN for the manager
Which of the following is true of a rainbow table? (Select TWO)
The rainbow table is built in real-time during the attack
Rainbow tables are the most effective online attack type
Rainbow tables require significant CPU cycles at attack time
Different tables are required for different hashing methods
A rainbow table won’t be useful if the passwords are salted
A server administrator at a bank has noticed a decrease in the number
of visitors to the bank's website. Additional research shows that users are
being directed to a different IP address than the bank's web server. Which
of the following would MOST likely describe this attack?
Disassociation
DDoS
Buffer overflow
DNS poisoning
Which of these cloud deployment models would share resources between
a private virtualized data center and externally available cloud services?
SaaS
Community
Hybrid
Containerization
A company hires a large number of seasonal employees, and their
system access should normally be disabled when the employee leaves
the company. The security administrator would like to verify that their
systems cannot be accessed by any of the former employees. Which of the
following would be the BEST way to provide this verification?
Confirm that no unauthorized accounts have administrator access
Validate the account lockout policy
Validate the processes and procedures for all outgoing employees
Create a report that shows all authentications for a 24-hour period
A network administrator has installed a new access point, but only a
portion of the wireless devices are able to connect to the network. Other
devices can see the access point, but they are not able to connect even
when using the correct wireless settings. Which of the following security
features was MOST likely enabled?
MAC filtering
SSID broadcast suppression
802.1X authentication
Anti-spoofing
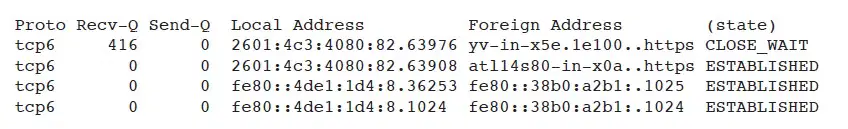
A security administrator has gathered this information:
Which of the following is being used to create this information?
tracert
netstat
dig
netcat
An attacker has discovered a way to disable a server by sending specially
crafted packets from many remote devices to the operating system. When
the packet is received, the system crashes and must be rebooted to restore
normal operations. Which of the following would BEST describe this
attack?
Privilege escalation
Spoofing
Replay attack
DDoS
A data breach has occurred in a large insurance company. A security
administrator is building new servers and security systems to get all of
the financial systems back online. Which part of the incident response
process would BEST describe these actions?
. Lessons learned
Isolation and containment
Reconstitution
Precursors
A manufacturing company has moved an inventory application from their
internal systems to a PaaS service. Which of the following would be the
BEST way to manage security policies on this new service?
DLP
SIEM
IPS
CASB
An organization has identified a significant vulnerability in a firewall
used for Internet connectivity. The firewall company has stated there are
no plans to create a patch for this vulnerability. Which of the following
would BEST describe this issue?
Lack of vendor support
Improper input handling
Improper key management
End-of-life
A company has decided to perform a disaster recovery exercise during an
annual meeting with the IT directors and senior directors. A simulated
disaster will be presented, and the participants will discuss the logistics
and processes required to resolve the disaster. Which of the following
would BEST describe this exercise?
After-action report
Business impact analysis
Alternate business practice
Tabletop exercise
A security administrator needs to identify all computers on the company
network infected with a specific malware variant. Which of the following
would be the BEST way to identify these systems?
Honeynet
Data masking
DNS sinkhole
DLP
A system administrator has been called to a system that is suspected to
have a malware infection. The administrator has removed the device from
the network and has disconnected all USB flash drives. Which of these
incident response steps is the administrator following?
Lessons learned
Containment
Detection
Reconstitution
How can a company ensure that all data on a mobile device is
unrecoverable if the device is lost or stolen?
Containerization
Geofencing
Screen locks
Remote wipe
A security administrator is collecting information associated with a
ransomware infection on the company's web servers. Which of the
following log files would provide information regarding the memory
contents of these servers?
Web
Packet
Dump
DNS
Which part of the PC startup process verifies the digital signature of the
OS kernel?
Measured Boot
Trusted Boot
Secure Boot
POST
Which of these best describes two-factor authentication?
A printer uses a password and a PIN
The door to a building requires a fingerprint scan
An application requires a TOTP code
A Windows Domain requires a username, password,
and smart card
A company is deploying a new mobile application to all of its employees
in the field. Some of the problems associated with this rollout include:
• The company does not have a way to manage the mobile devices
in the field
• Company data on mobile devices in the field introduces additional risk
• Team members have many different kinds of mobile devices
Which of the following deployment models would address
these concerns?
Corporate-owned
COPE
VDI
BYOD
An organization is installing a UPS for their new data center. Which of
the following would BEST describe this type of control?
Compensating
Preventive
Administrative
Detective
A manufacturing company would like to track the progress of parts as
they are used on an assembly line. Which of the following technologies
would be the BEST choice for this task?
Quantum computing
Blockchain
Hashing
Asymmetric encryption
A security administrator has been asked to respond to a potential security
breach of the company’s databases, and they need to gather the most
volatile data before powering down the database servers. In which order
should they collect this information?
CPU registers, temporary files, memory, remote monitoring data
Memory, CPU registers, remote monitoring data, temporary files
Memory, CPU registers, temporary files, remote monitoring data
CPU registers, memory, temporary files, remote monitoring data
A Linux administrator is downloading an updated version of her Linux
distribution. The download site shows a link to the ISO and a SHA256
hash value. Which of these would describe the use of this hash value?
Verifies that the file was not corrupted during the file transfer
Provides a key for decrypting the ISO after download
Authenticates the site as an official ISO distribution site
Confirms that the file does not contain any malware
A company's security policy requires that login access should only
be available if a person is physically within the same building as the
server. Which of the following would be the BEST way to provide this
requirement?
TOTP
Biometric scanner
PIN
SMS
Your development team has installed a new application and database to
a cloud service. After running a vulnerability scanner on the application
instance, you find that the database is available for anyone to query
without providing any authentication. Which of these vulnerabilities is
MOST associated with this issue?
Improper error handling
Open permissions
Race condition
Memory leak
Employees of an organization have received an email offering a cash
bonus for completing an internal training course. The link in the email
requires users to login with their Windows Domain credentials, but the
link appears to be located on an external server. Which of the following
would BEST describe this email?
Whaling
Vishing
Smishing
Phishing
Which of the following risk management strategies would include the
purchase and installation of an NGFW?
Transference
Mitigation
Acceptance
Risk-avoidance
Which of the following would be the BEST way to confirm the secure
baseline of a deployed application instance?
Compare the production application to the sandbox
Perform an integrity measurement
Compare the production application to the previous version
Perform QA testing on the application instance
A member of the accounting team was out of the office for two weeks,
and an important financial transfer was delayed until they returned.
Which of the following would have prevented this delay?
Split knowledge
Least privilege
Job rotation
Dual control
A security analyst has identified a number of sessions from a single IP
address with a TTL equal to zero. One of the sessions has a destination of
the Internet firewall, and a session immediately after has a destination of
your DMZ server. Which of the following BEST describes this
log information?.
.Someone is performing a vulnerability scan against the firewall and DMZ server
Users are performing DNS lookups
A remote user is grabbing banners of the firewall and DMZ server
Someone is performing a traceroute to the DMZ server
A security analyst has identified a number of sessions from a single IP
address with a TTL equal to zero. One of the sessions has a destination of
the Internet firewall, and a session immediately after has a destination of
your DMZ server. Which of the following BEST describes this
log information?
Someone is performing a vulnerability scan against the
firewall and DMZ server
Users are performing DNS lookups
A remote user is grabbing banners of the firewall and DMZ server
Someone is performing a traceroute to the DMZ server
An attacker has sent more information than expected in a single API
call, and this has allowed the execution of arbitrary code. Which of the
following would BEST describe this attack?
Buffer overflow
Replay attack
Session hijacking
DDoS
A company encourages users to encrypt all of their confidential materials
on a central server. The organization would like to enable key escrow as a
backup. Which of these keys should the organization place into escrow?
Private
CA
Session
Public
A security administrator is designing an authentication process for a
new remote site deployment. They would like the users to provide their
credentials when they authenticate in the morning, and they do not want
any additional authentication requests to appear during the rest of the
day. Which of the following should be used to meet this requirement?
TACACS+
LDAPS
Kerberos
802.1X
A manufacturing company would like to use an existing router to
separate a corporate network and a manufacturing floor that use the same
physical switch. The company does not want to install any additional
hardware. Which of the following would be the BEST choice for this
segmentation?
Connect the corporate network and the manufacturing floor
with a VPN
Build an air gapped manufacturing floor network
Use personal firewalls on each device
Create separate VLANs for the corporate network and the
manufacturing floor
When a home user connects to the corporate VPN, they are no longer
able to print to their local network printer. Once the user disconnects
from the VPN, the printer works normally. Which of the following would
be the MOST likely reason for this issue?
The VPN uses IPSec instead of SSL
Printer traffic is filtered by the VPN client
The VPN is stateful
The VPN tunnel is configured for full tunnel
A data center manager has built a Faraday cage in the data center, and a
set of application servers have been placed into racks inside the Faraday
cage. Which of the following would be the MOST likely reason for the
data center manager to install this configuration of equipment?
Protect the servers against any unwanted electromagnetic fields
Prevent physical access to the servers without the proper credentials
Provide additional cooling to all devices in the cage
Adds additional fire protection for the application servers
A recent report shows the return of a vulnerability that was previously
patched four months ago. After researching this issue, the security team
has found that a recent patch has reintroduced this vulnerability on
the servers. Which of the following should the security administrator
implement to prevent this issue from occurring in the future?
Templates
Elasticity
Master image
Continuous monitoring
A security manager would like to ensure that unique hashes are used with
an application login process. Which of the following would be the BEST
way to add random data when generating a set of stored password hashes?
Salting
Obfuscation
Key stretching
Digital signature
Which cryptographic method is used to add trust to a digital certificate?
X.509
Hash
Symmetric encryption
Digital signature
An MSP is designing a new server room for a large company. Which of
the following should be included in the design to provide redundancy?
(Select TWO)
SIEM
Temperature monitors
RAID arrays
Dual power supplies
Hot and cold aisles
An organization maintains a large database of customer information for
sales tracking and customer support. Which person in the organization
would be responsible for managing the access rights to this data?
Data processor
Data owner
Privacy officer
Data custodian
An organization’s content management system (CMS) currently labels
files and documents as “Unclassified” and “Restricted.” On a recent
updated to the CMS, a new classification type of “PII” was added. Which
of the following would be the MOST likely reason for this addition?
Healthcare system integration
Simplified categorization
Expanded privacy compliance
Decreased search time
A corporate security team would like to consolidate and protect the
certificates across all of their web servers. Which of these would be the
BEST way to securely store these certificates?
Use an HSM
Implement full disk encryption on the web servers
Use a TPM
Upgrade the web servers to use a UEFI BIOS
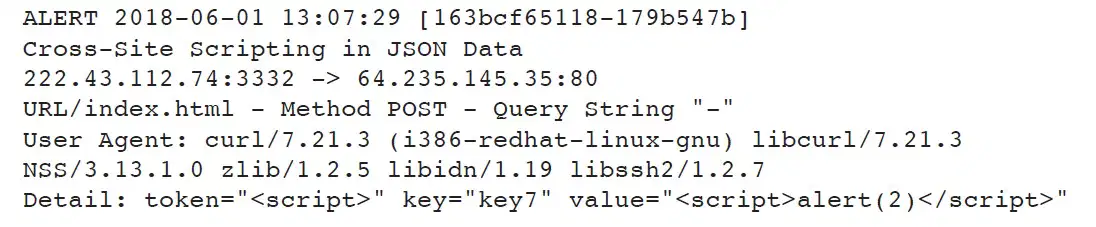
Jennifer is reviewing this security log from her IPS:
Which of the following can be determined from this log information?
(Select TWO)
The alert was generated from a malformed User Agent header
The alert was generated from an embedded script
The attacker’s IP address is 222.43.112.74
The attacker’s IP address is 64.235.145.35
The alert was generated due to an invalid client port number
Which of the following describes a monetary loss if one event occurs?
ALE
SLE
RTO
ARO
A user with restricted access has typed this text in a search field of an
internal web-based application:
USER77' OR '1'='1
After submitting this search request, all of the database records are
displayed on the screen. Which of the following would BEST describe
this search?
CSRF
Buffer overflow
SQL injection
SSL stripping
A user has opened a helpdesk ticket complaining of poor system
performance, excessive pop up messages, and the cursor moving
without anyone touching the mouse. This issue began after they opened
a spreadsheet from a vendor containing part numbers and pricing
information. Which of the following is MOST likely the cause of this
user's issues?
On-path
Worm
RAT
Logic bomb
A web-based manufacturing company processes monthly charges to credit
card information saved in the customer's profile. Which of the following
standards would be required to maintain this payment information?
GDPR
ISO 27001
PCI DSS
CSA CCM
A security manager has created a report showing intermittent network
communication from external IP addresses to certain workstations on the
internal network. These traffic patterns occur at random times during the
day. Which of the following would be the MOST likely reason for these
traffic patterns?
ARP poisoning
Backdoor
Polymorphic virus
Trojan horse
The security policies in a manufacturing company prohibit the
transmission of customer information. However, a security administrator
has received an alert that credit card numbers were transmitted as an
email attachment. Which of the following was the MOST likely source
of this alert message?
IPS
DLP
SMTP
IPsec
A security administrator has configured a virtual machine in a screened
subnet with a guest login account and no password. Which of the
following would be the MOST likely reason for this configuration?
The server is a honeypot for attracting potential attackers
The server is a cloud storage service for remote users
The server will be used as a VPN concentrator
The server is a development sandbox for third-party
programming projects
A company's outgoing email server currently uses SMTP with no
encryption. The security administrator would like to implement
encryption between email clients without changing the existing
server-to-server communication. Which of the following would be the
BEST way to implement this requirement?
Implement Secure IMAP
Require the use of S/MIME
Install an SSL certificate on the email server
Use a VPN tunnel between email clients
A company would like to securely deploy applications without the
overhead of installing a virtual machine for each system. Which of the
following would be the BEST way to deploy these applications?
Containerization
IaaS
Proxies
CASB
A company has just purchased a new application server, and the security
director wants to determine if the system is secure. The system is currently
installed in a test environment and will not be available to users until the
rollout to production next week. Which of the following would be the
BEST way to determine if any part of the system can be exploited?
Tabletop exercise
Vulnerability scanner
Password cracker
Penetration test

