
 Worksheets
Cryptography Quiz
Total questions: 52
Worksheet time: 26mins
What is the primary concern addressed by cryptography according to the text?
Protecting information through transformation to prevent unauthorized reading.
Enhancing the speed of data transmission.
Improving the aesthetic design of written communication.
Developing new languages for ancient societies.
Which ancient civilizations are mentioned as examples of using cryptographic systems?
Ancient Egypt and Ancient India.
Ancient Greece and Ancient Rome.
Ancient China and Ancient Mesopotamia.
Ancient Persia and Ancient Babylon.
What was initially considered a cryptographic system in ancient societies?
Writing itself.
Spoken language.
Mathematical calculations.
Religious rituals.
Why was cryptography limited to certain individuals in ancient societies?
It was considered sacred and reserved for the chosen few.
It was too complex for the general population to understand.
It required advanced technology unavailable to most people.
It was used exclusively for trade and commerce.
What is the primary purpose of cryptographic methods for information protection?
To make information accessible to everyone.
To ensure information is unavailable without a cryptographic key.
To store information in plain text for easy access.
To delete information permanently.
Which of the following best describes the reliability of cryptographic methods for information protection?
Cryptographic methods are unreliable and prone to errors.
Cryptographic methods protect access to information rather than the information itself.
Cryptographic methods are the most reliable as they directly protect the information itself.
Cryptographic methods are outdated and rarely used.
How are cryptographic methods typically implemented?
Through manual encryption techniques.
Through software programs or program packages.
Through physical locks and keys.
Through verbal agreements.
What happens to the content of information when cryptographic methods are applied?
The content becomes accessible to everyone.
The content remains unchanged but is hidden.
The content becomes inaccessible without the cryptographic key.
The content is permanently deleted.
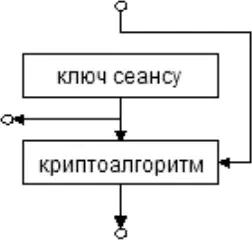
What is the main characteristic of symmetric cryptosystems?
They use different keys for encryption and decryption.
They use the same key for both encryption and decryption.
They do not require a key for encryption.
They use multiple keys for encryption and decryption.
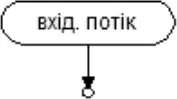
What is the process of converting original text into encrypted text called?
Decryption
Hashing
Encryption
Archiving
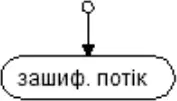
What is the reverse process of encryption called?
Hashing
Decryption
Archiving
Coding
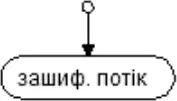
In symmetric cryptosystems, what is the encrypted text called?
Original text
Open text
Cipher text
Session key
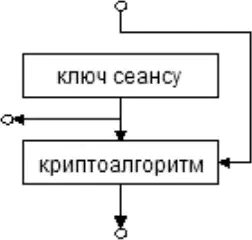
What is the role of the key in symmetric cryptosystems?
It is used only for encryption.
It is used only for decryption.
It is used for both encryption and decryption.
It is not used in symmetric cryptosystems.
What type of keys are used in cryptosystems with an open key?
Public and private keys
Symmetric and asymmetric keys
Encryption and decryption keys
Random and fixed keys
How is information encrypted in cryptosystems with an open key?
Using the private key
Using the public key
Using both public and private keys simultaneously
Using a random key
Who has access to the public key in cryptosystems with an open key?
Only the sender
Only the receiver
Everyone who wants to encrypt information
Only authorized users
How is information decrypted in cryptosystems with an open key?
Using the public key
Using the private key
Using both public and private keys simultaneously
Using a random key
What is the primary function of a hash function?
To convert input data of any size into fixed-size data.
To encrypt data for secure communication.
To store data in a database.
To compress data for storage.
What is hashing commonly used for?
Transforming input data of arbitrary length into a fixed-length bit string.
Encrypting data for secure transmission.
Sorting data in ascending order.
Compressing files for storage.
What is another term for the result of a hash function?
Hash code
Encryption key
Data packet
File compression
Which of the following is NOT a term associated with hashing?
Hash sum
Message digest
Hash code
Data encryption
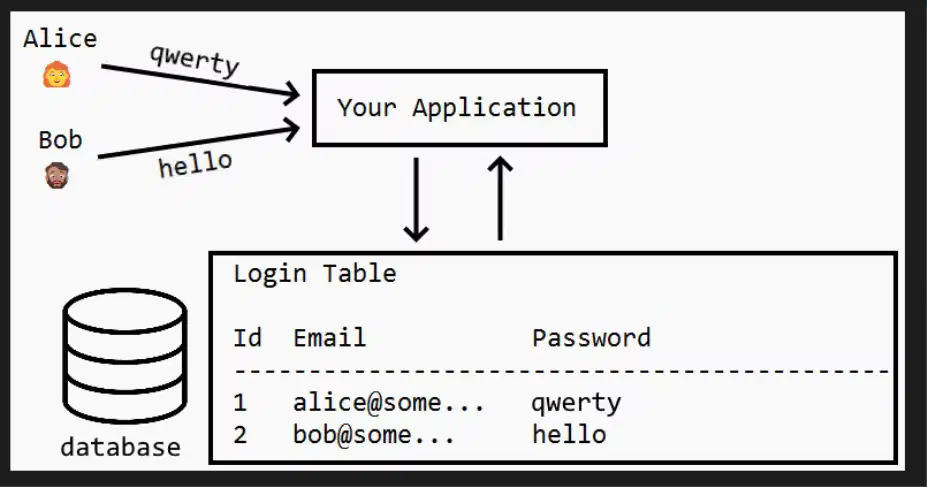
What is the purpose of the "Login Table" in the given diagram?
To store user credentials such as email and password.
To store application data unrelated to users.
To store encrypted files for the application.
To store user preferences for the application.
What is the potential risk shown in the second diagram involving the hacker?
The hacker can access encrypted passwords and potentially decrypt them.
The hacker can delete the database entirely.
The hacker can modify user preferences in the application.
The hacker can block users from accessing the application.
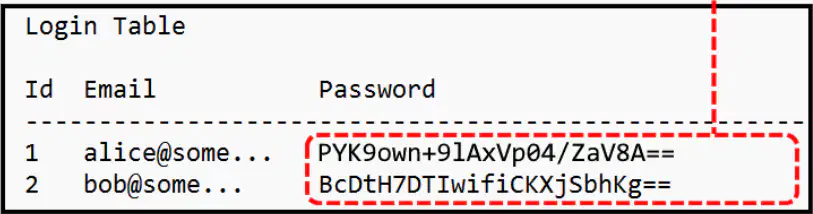
Why is it important to encrypt passwords in the database as shown in the second diagram?
To prevent hackers from easily accessing user credentials.
To make the database faster.
To reduce the size of the database.
To allow users to recover their passwords easily.
What does the term "Your Application" represent in the diagram?
The software that interacts with the database to authenticate users.
A hardware device used to store user data.
A tool for encrypting passwords.
A server used for hosting websites.
What is the role of the database in the context of the diagram?
To store and manage user credentials securely.
To process user requests directly.
To act as a firewall for the application.
To encrypt passwords automatically.
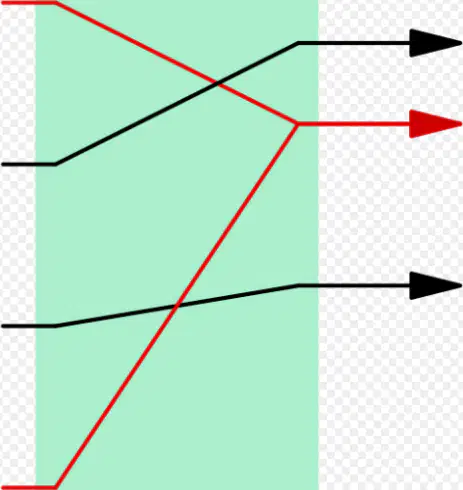
What is the purpose of a hash function as shown in the diagram?
To encrypt data for security purposes.
To map keys to specific hash values for efficient data retrieval.
To sort data alphabetically.
To generate random numbers for programming.
Which of the following is an example of a key in the diagram?
01
John Smith
Hash function
15
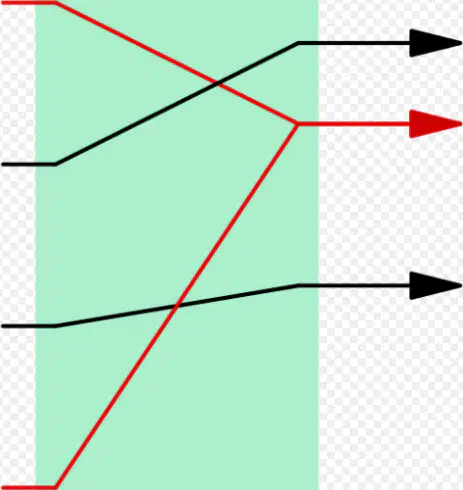
What is the range of hash values generated by the hash function in the diagram?
00 to 10
00 to 15
01 to 20
01 to 15
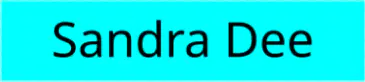
Which key in the diagram maps to the hash value "02"?
John Smith
Lisa Smith
Sandra Dee
Sam Doe
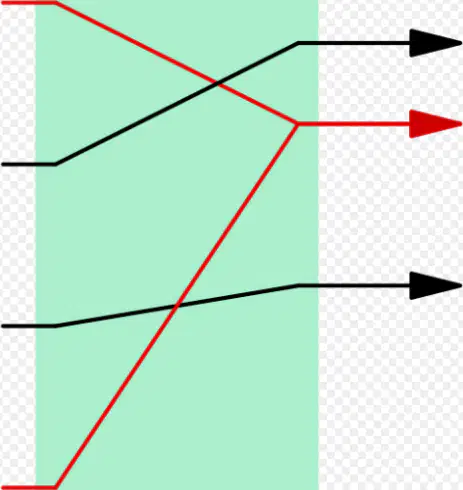
What is the primary benefit of using hash functions in data structures?
To ensure data security.
To reduce memory usage.
To enable quick data retrieval.
To sort data efficiently.
What is the purpose of an electronic signature system?
To encrypt messages for secure communication.
To verify authorship and authenticity of a message.
To store data securely in a database.
To create digital art using binary code.
What is attached to the text in an electronic signature system?
Cryptographic transformation.
A digital watermark.
A password.
A QR code.
Which of the following is NOT a function of an electronic signature system?
Verifying the authenticity of a message.
Checking the authorship of a message.
Encrypting the message for secure communication.
Allowing unauthorized access to the message.
What is a key requirement for modern cryptographic systems to ensure information security?
Encrypted messages should only be readable with the presence of a key.
Encrypted messages should be readable without a key.
Encrypted messages should be accessible to everyone.
Encrypted messages should not require any key for decoding.
What is the primary requirement for the number of operations needed to decrypt information using various keys?
It should exceed the capabilities of modern computers, including network calculations.
It should match the capabilities of modern computers.
It should be less than the capabilities of modern computers.
It should not consider network calculations.
What should not affect the reliability of encryption security?
Knowledge of the encryption algorithm
The type of device used for encryption
The length of the encrypted message
The number of encryption keys used
What should a minor change in the encryption key NOT lead to?
Significant changes in the encrypted message
Improved encryption security
Faster decryption process
Reduced reliability of the algorithm
What characteristic should structural elements of an encryption algorithm have?
They should be unchangeable
They should vary with each encryption
They should depend on the message length
They should be randomly generated
What is the main weakness of cryptographic systems with open keys during practical implementation?
The complexity of the algorithm.
The problem of key distribution.
The speed of encryption.
The size of the encrypted data.
What is required for the exchange of confidential information between two subjects in an information system?
Both subjects must use the same encryption algorithm.
A key must be generated by one subject and securely transferred to the other.
Both subjects must use different encryption keys.
The information must be encrypted twice for security.
What is the main concept behind the cryptosystem described in the text?
The use of a single key for encryption and decryption.
The generation of two keys, one public and one private, linked by a specific rule.
The use of classical algebra only for encryption.
The sharing of secret keys openly with all users.
What is the purpose of the public key in the cryptosystem?
To encrypt messages and make them accessible to everyone.
To decrypt messages sent by the sender.
To be published and accessible to anyone who wants to send a message to the recipient.
To store secret information securely.
Where is the private key stored in the cryptosystem?
It is shared with everyone.
It is stored securely by the recipient.
It is published alongside the public key.
It is used only for encryption purposes.
What mathematical foundation is used in the described cryptosystem?
Classical algebra only.
Modern algebra only.
Both classical and modern algebra.
No mathematical foundation is used.
What is the principle of encryption described in the text?
The original text is encrypted with a public key and can be decrypted with the same public key.
The original text is encrypted with a public key and can only be decrypted with a private key known to the recipient.
The original text is encrypted with a private key and can be decrypted with the same private key.
The original text is encrypted with a private key and can only be decrypted with a public key.
Why is the private key important in the encryption process described?
It is used to encrypt the original text.
It is used to decrypt the encrypted text and is known only to the recipient.
It is used to share the encrypted text with others.
It is used to replace the public key in the encryption process.
What is the main characteristic of the encrypted text in the described principle?
It can be decrypted using the same public key used for encryption.
It cannot be decrypted using the same public key used for encryption.
It can be decrypted using any key available to the sender.
It cannot be decrypted by the recipient.
What is the first step in establishing an HTTPS connection according to the diagram?
The server sends a session key to the browser.
The browser generates a session key and encrypts it.
You enter the website address in the browser.
The server decrypts the session key with a private key.
What does the server send to the browser in the second step of HTTPS connection establishment?
A session key.
A private key.
An open key.
An encrypted message.
What happens after the browser generates a session key in the third step?
The browser sends the session key to the server without encryption.
The browser encrypts the session key with the open key and sends it to the server.
The server encrypts the session key and sends it back to the browser.
The browser decrypts the session key and sends it to the server.
What does the server do in the final step of HTTPS connection establishment?
The server generates a session key and sends it to the browser.
The server decrypts the session key with a private key and confirms the HTTPS connection.
The server encrypts the session key and sends it back to the browser.
The server sends an open key to the browser.

