
 Worksheets
FORTIEDR
Total questions: 44
Worksheet time: 27mins
What is the purpose of the Threat Hunting feature?
Delete any file from any collector in the organization
Find and delete all instances of a known malicious file or hash in the organization
Identify all instances of a known malicious file or hash and notify affected users
Execute playbooks to isolate affected collectors in the organization
A FortiEDR security event is causing a performance issue with a third-parry application. What must you do first about the event?
Contact Fortinet support
Terminate the process and uninstall the third-party application
Immediately create an exception
Investigate the event to verify whether or not the application is safe
Which two types of remote authentication does the FortiEDR management console support?(Choose two.)
Radius
SAML
TACACS
LDAP
How does FortiEDR implement post-infection protection?
By preventing data exfiltration or encryption even after a breach occurs
By using methods used by traditional EDR
By insurance against ransomware
By real-time filtering to prevent malware from executing
What is the benefit of using file hash along with the file name in a threat hunting repository search?
It helps to make sure the hash is really a malware
It helps to check the malware even if the malware variant uses a different file name
It helps to find if some instances of the hash are actually associated with a different file
It helps locate a file as threat hunting only allows hash search
An administrator needs to restrict access to the ADMINISTRATION tab in the central manager for a specific account. What role should the administrator assign to this account?
ADMIN
USER
LOCAL ADMIN
REST API
Which connectors can you use for the FortiEDR automated incident response? (Choose two.)
FortiNAC
FortiGate
FortiSiem
FortiSandbox
What is true about classifications assigned by Fortinet Cloud Service(FCS)?
The core is responsible for all classifications if FCS playbooks are disabled
The core only assigns a classification if FCS is not available
FCS revises the classification of the core based on its database
FCS is responsible for all classifications
A company requires a global communication policy for a FortiEDR multi-tenant environment. How can the administrator achieve this?
An administrator creates a new communication control policy and shares it with other organizations
A local administrator creates new a communication control policy and shares it with other organizations
A local administrator creates a new communication control policy and assigns it globally to all organizations
An administrator creates a new communication control policy for each organization
Which two statements are true about the remediation function in the threat hunting module? (Choose two.)
The file is removed from the affected collectors
The threat hunting module sends the user a notification to delete the file
The file is quarantined
The threat hunting module deletes files from collectors that are currently online.
The FortiEDR core classified an event as inconclusive, but a few seconds later FCS revised the classification to malicious. What playbook actions ate applied to the event?
Playbook actions applied to inconclusive events
Playbook actions applied to handled events
Playbook actions applied to suspicious events
Playbook actions applied to malicious events
Which threat hunting profile is the most resource intensive?
Comprehensive
Inventory
Default
Standard Collection
FortiXDR relies on which feature as part of its automated extended response?
Playbooks
Security Policies
Forensic
Communication Control
What is the role of a collector in the communication control policy?
A collector blocks unsafe applications from running
A collector is used to change the reputation score of any application that collector runs
A collector records applications that communicate externally
A collector can quarantine unsafe applications from communicating
An administrator finds a third party free software on a user's computer mat does not appear in me application list in the communication control console Which two statements are true about this situation? (Choose two)
The application is allowed in all communication control policies
The application is ignored as the reputation score is acceptable by the security policy
The application has not made any connection attempts
The application is blocked by the security policies
Which scripting language is supported by the FortiEDR action managed?
TCL
Python
Perl
Bash
Which FortiEDR component is required to find malicious files on the entire network of an organization?
FortiEDR Aggregator
FortiEDR Central Manager
FortiEDR Threat Hunting Repository
FortiEDR Core
Which security policy has all of its rules disabled by default?
Device Control
Ransomware Prevention
Execution Prevention
Exfiltration Prevention
Which two statements about the FortiEDR solution are true? (Choose two.)
It provides pre-infection and post-infection protection
It is Windows OS only
It provides central management
It provides pant-to-point protection
with respect to operating fortiedr, what does proactive risk mitigation refer to ?
automatically blocking users from installing unauthorized applications
automatically blocking endpoints from communicating to network resources
automatically blocking applications from communicating if they have a poor reputation or CVE score
automatically blocking communication from all applications unless they are specifically enabled
Which fortiedr protection uses NGAV functionality?
incident response
pre-infection
risk mitigation
post-infection
Which three steps does FortiXDR perform to find and prevent cyberattacks?
Extended analysis
Extended Detection
Extended discovery
Extended investigation
extended response
which statements is true about the flow analyzer view in forensics?
it displays a graphic flow diagram
two events can be compared side by side
it shows details about processes and sub processes
the stack memory of specific device can be retrieved
a company requires a global exception for a fortiedr multi tenant environment how can the administrator achieve this ?
the local administrator can create a new exception and share it with other organizations
a user account can create a new exception and share it with other organizations
the administrator can create a new exception and assign it globally to all organizations
the admintrator can create a new exception policy for each organization hosted on fortiedr
which two investigation issues requires a full memory dump of the fortiedrcollector ?
system hang issue
third party application issues
system crash issue
collector and core connectivity issue events
how does the fortiedr approach compare to the traditional EDR?
FortiEDR blocks threats in real time eliminating the response gap
traditional EDR is faster
there is no difference in response time
FortiEDR requires less staff
which two events can tigger fortiedr ngav policy violations?
when a malicious file attempts to communicate externally
when a malicious file executed
when a malicious file is read
when a malicious file attempts to access data
which two types of traffic are allowed while the device is in isolation mode
outgoing ssh connections
http sessions
icmp sessions
incoming RDP connections
which fortiedr component must have jumpbox functionality to connect with fortianalyzer
collector
core
central manager
aggregator
when installing a fortiedr collector why is a registration password for collectors needed
to restrict installation and uninstallation of collectors
to verify fortinet support request
to restrict access to the management console
to verify new group assignment
an administrator finds that a newty installed collector does not display on the inventory tab in the central manager what two troubleshooting steps must the administrator perform
export the collector logs from the central manager
verify the central manager has connectivity to FCS
verify TCP port 8081 and 555 are open
check if the fortiedr services are running on the collector device
which two criteria are requirements of integrating fortiedr into the fortinet security fabric
core with core only functionality
a forensics add on license
central manager connected to FCS
A valid APi user with access to connectors

what is true about the payroll manager exe eventa
an event has not been handled by a console admin
an event has been deleted
a rule assigned action is get to block but the policy is in simulation mode
an event has been handled by the communication control policy

based on the event exception shown in the exhibit which two statements about the exception are true
FCS playbook is enable by fortinet support
the system owner can modify the trigger rules parameters
the exception is applied only on device C8092231196
a partial exception is applied to this event

based on postman outputshown in the exhibit why is the user getting an unathorized
postman cannot reach the central manager
api access is disabled on the central manager
the user has been assigned admin and rest api roles
fortiedr requires a password reset the first time a user logs in

the exhibits show the collector state and active connections the collector is unable to connect to aggregator ip address 10.160.6.100 using default port based on the netstat command outout what must you do to resolve the connectivity issue
reinstall collector agent and use port 555
reinstall collector agent and use port 443
reinstall collector agent and use port 6514
reinstall collector agent and use port 8081

an exception has been created for this event
the device has been isolated
the exfiltration prevention policy been blocked this event
the forensics data displayed in the stacks view

the policy is in simulation mode
the device is moved to isolation
the event has been block
playbooks is configured for this event

the exhibits show application policy logs and application details collector C8092231196 is a member of the finance group what must an administrator do to block the filezilla application
deny application in finance policy
assign finance policy to dba group
assign finance policy to default collector group
assing simulation communication control policy to dba group

based on the threat hunting event details shown in the exhibit which two statements about the event are true
the activity event is associated with the file action
the user fortinet has executed a ping command
the ping exe process was blocked
there are no mitre details available for this event
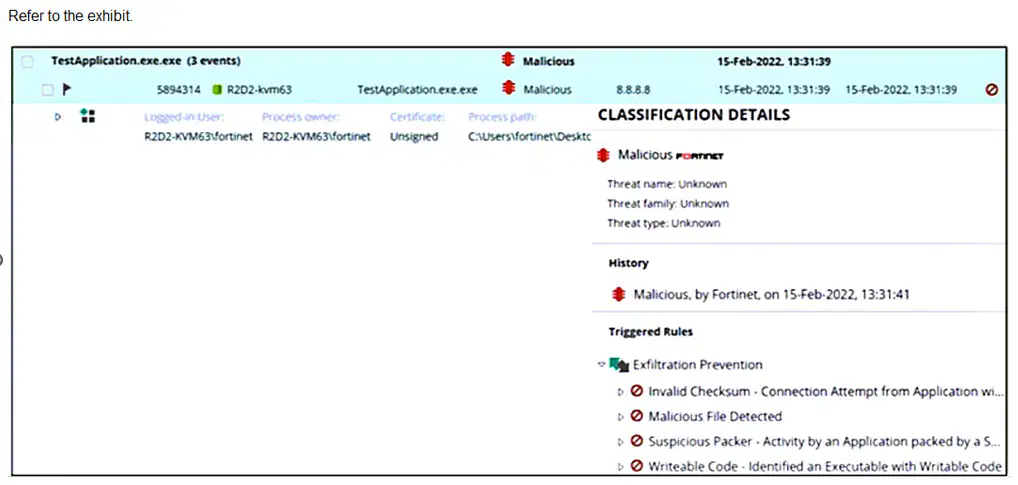
based on the event shown in the exhibit which two statements about the event are true
the ngav policy has blocked testapplication exe
fcs classified the event as malicious
testapplication.exe is sophisticated malware
the user was able to launch testapplication.exe
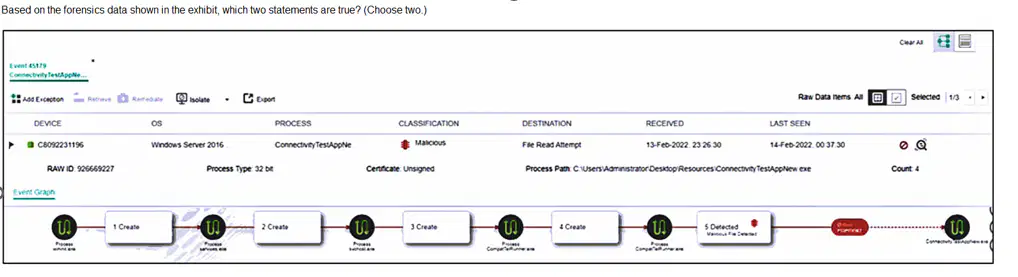
the device cannot be remediated
the execution prevention policy has blocked this event
the event was blocked because the certificate is unsigned
device c8092231196 has been isolated

based on the threat hunting query shown in the exhibit, which of the following is true
a security event will be triggered when the device attempts a rdp connection
this query is included in other organizations
the query will only check for network category
rdp connections will be blocked and classfied as suspicious

based on the fortiedr status output shown in the exhibit which two statements about the fortiedr collector are true
the collector device has windows firewall enabled
the collector has been installed with an incorrect port number
the collector has been installed with an incorrect resgistration password
the collector device cannot reach the central manager

